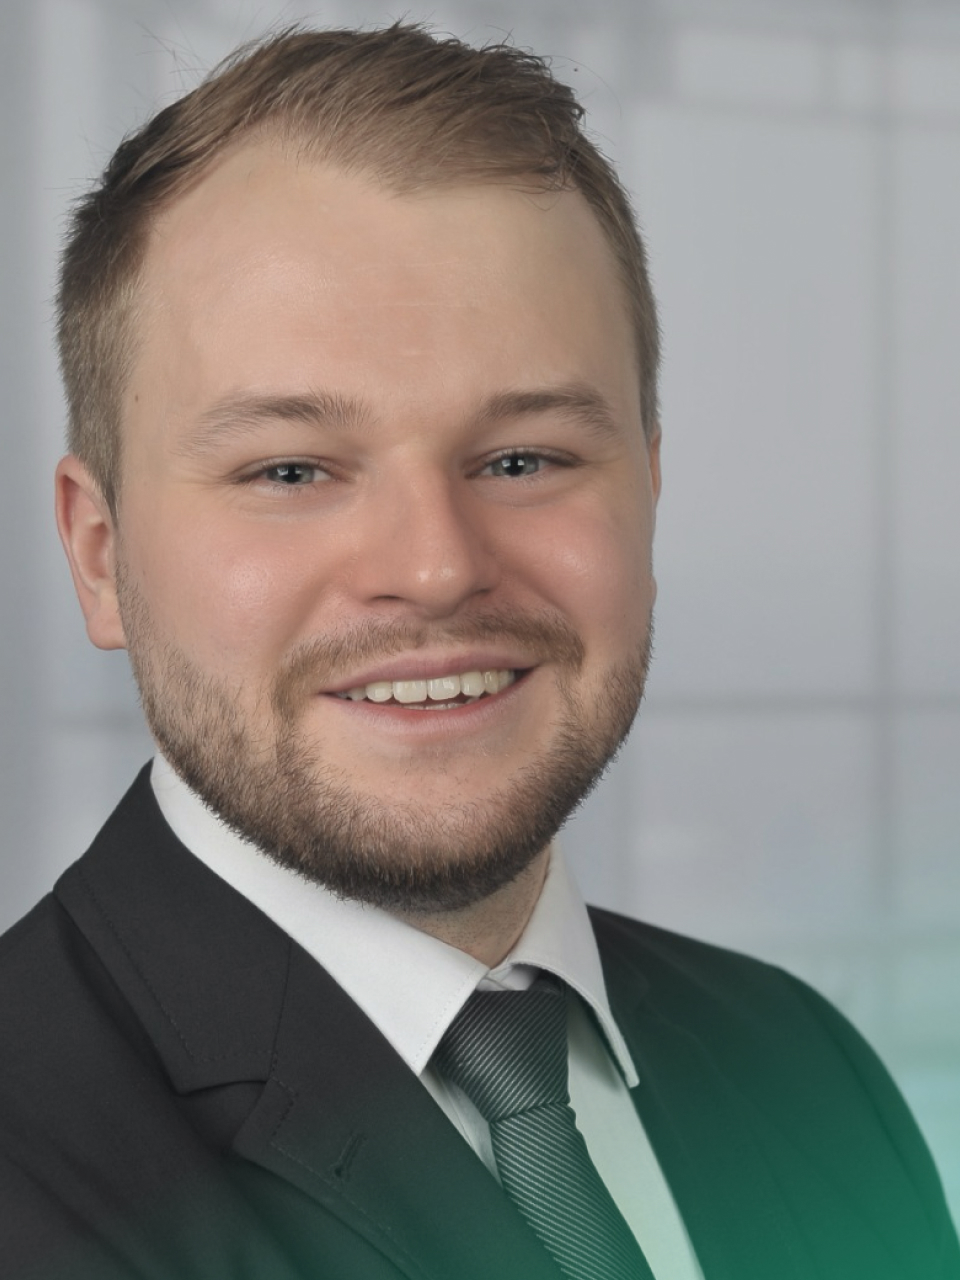
Santhosh Komaragiri
Founder & CEO
After years across security and compliance, Santhosh started DocsOrb so AI policy is something a company can run — visible, owned, and enforced.
AI has become part of how companies think, decide and operate.
That excites me! It also makes one question impossible to ignore:
Can we trust it?
We learned to trust networks, payments, cloud infrastructure and digital identities because we built systems around them. Boundaries. Controls. Accountability. Ways to know what should happen, and what should never happen.
AI needs the same foundation.
I started DocsOrb because I believe companies should be able to use increasingly powerful AI without giving up control over how it behaves, what it accesses, or the decisions it influences.
Our obsession is simple: make AI trustable.
Trustable for the people working with it.
Trustable for the companies depending on it.
Trustable for the customers affected by it.
As AI becomes more capable and autonomous, this will only matter more.
DocsOrb is our contribution to building that future.
Santhosh Komaragiri
Founder, DocsOrb
Founder & CEO
After years across security and compliance, Santhosh started DocsOrb so AI policy is something a company can run — visible, owned, and enforced.
Founding Partner, ISO Certified Expert
Brings standards discipline to how DocsOrb designs governance that can be shown, not only written.
Founding Legal Partner
Rechtsanwältin and partner at LEGAL DPT in Munich.
Founding Legal Partner
Rechtsanwältin and partner at LEGAL DPT, admitted in Germany, Portugal, and Brazil.
Advisor
ISO 27001 / 27701, 42001, TISAX, BCM, NIS2, DORA, Senior Lead Auditor
Precise thinking, plain language, and honest communication. No buzzwords, noise, or complexity for its own sake.
We earn trust by being careful with legal nuance, product quality, privacy, and the details customers depend on.
People who take initiative, close loops, and improve the system around them, instead of waiting for perfect conditions.
We say what DocsOrb does, and what it does not. Governance should be understandable to legal, security, and the people using AI.
We treat AI use as something organisations want to enable safely. The work is a habit a team can run, not a poster.
Legal nuance, privacy, and product quality are the job. Trust is earned in those details.
Feedback belongs in the work, while a decision can still change. A small team has no room for politics.
We protect attention. Finish what is open before starting the next thread.
The agenda comes from a real organisation using AI. We do not build process for its own sake.
Make safe and responsible AI adoption operational for every organisation.
We value your privacy
We use cookies to keep DocsOrb secure, understand how the site is used, and improve your experience. You can accept all, reject optional cookies, or manage your preferences. Read our Privacy Policy